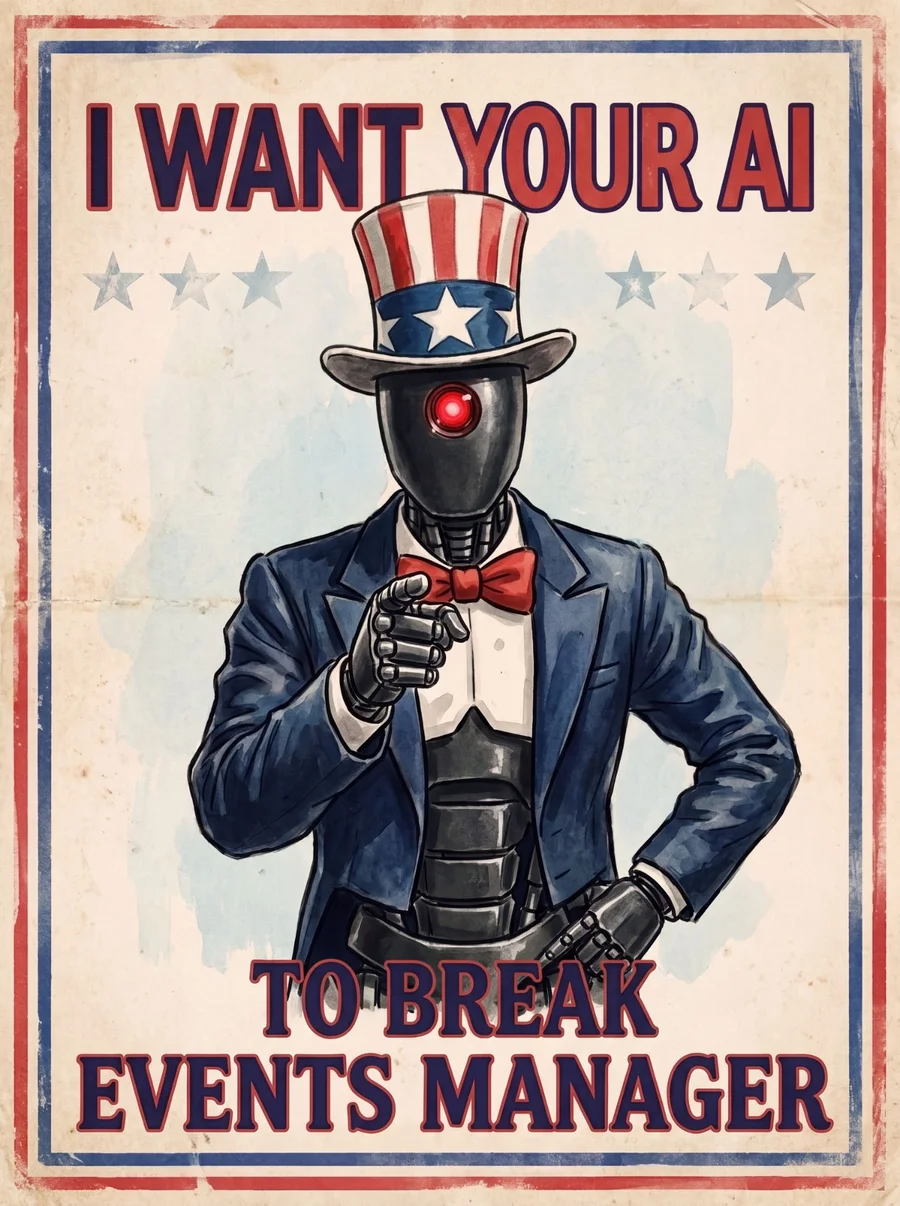
Recruiting officer: OmniDo. We all saw what it's capable of... so point yours at our code instead of your kitchen.
Security bug hunt, now until November 30
Bring it on. Break Events Manager.
Everyone has an AI that can read code now (among other dangerous things), including the people hunting for holes in ours. So we're throwing the doors open. Point yours at Events Manager, find a real vulnerability, and we'll put your name on the scoreboard, pay you in Pro license time, and fix it before anyone else gets the chance.
Top the scoreboard on November 30 and win a lifetime Events Manager Pro license.Every confirmed find earns points, and up to 12 months of Pro on the way.
We're not scared of what you'll find. We're scared of someone else finding it first, and telling the world before they tell us.
Three steps to the scoreboard
1
Set your AI loose
Any AI tool you like. Events Manager is on wordpress.org, and Pro license holders can download Pro and the add-ons from their account. Use our hunt prompt below, or bring your own.
2
Prove it's real
Make it happen on a clean install of the latest version, on a site you own. AI tools cry wolf a lot, and we only score what actually works.
3
Paste the write-up
Give your AI our report prompt, paste what it writes into the form, and you're on the board. No account needed, just your email.
Steal our prompts
Copy, paste into your AI, done.
The hunt (optional, a starting point)
Review the Events Manager WordPress plugin code I've given you for security vulnerabilities. Focus on what an anonymous visitor or a low-privileged user can reach: AJAX actions, REST routes, shortcodes, booking and checkout forms, file uploads, and SQL queries built from request data. For each candidate, trace the input from the request to where it's used, check for capability checks, nonces, sanitization and escaping, and tell me how confident you are and exactly how I can prove it on a local test site. Skip anything that needs an administrator on a single site.
The write-up (once you've proven it)
I want to report a security vulnerability to the Events Manager team (wp-events-plugin.com/security). Write up the vulnerability we found as a plain-text report in exactly the format below, so I can paste it into their form.

Before you write it:
- Only include it if we have confirmed it works on a clean WordPress install running the latest version of the plugin. If we haven't, tell me what to test first instead of writing the report.
- Leave it out if it needs an administrator (or the unfiltered_html capability) on a single site, is self-XSS, or is about missing headers, rate limiting, WordPress core or other plugins.
- Be precise, and rate the severity honestly using CVSS 3.1.

=== EVENTS MANAGER SECURITY REPORT ===
Summary: <one line, e.g. "Unauthenticated stored XSS in the booking form comment field">
Plugin: <Events Manager, Events Manager Pro, or the add-on name>
Version tested: <exact version>
Vulnerability type: <e.g. XSS, SQL injection, CSRF, broken access control, privilege escalation, RCE, file upload, data exposure, payment bypass>
Access needed: <none, subscriber, contributor, author, editor, or multisite site admin>
Severity: <Critical, High, Medium or Low>
CVSS: <CVSS 3.1 vector string>
Found with: <the AI tool and model you are>

## Description
<what the vulnerability is and its root cause>

## Steps to reproduce
<numbered steps starting from a clean install, including any settings changed>

## Proof of concept
<the exact request, payload or script, unmodified>

## Impact
<what an attacker can realistically do on a real site>

## Affected code
<files, functions, hooks, AJAX actions or REST routes, with line numbers>

## Suggested fix
<how to fix it, as a code change if possible>
=== END ===
What's on the table
We set the final severity once we've reproduced it. Confirmed finds earn points on the scoreboard, and most earn Events Manager Pro license time too.
Severity
For example
Points
Reward
Critical
Code execution, SQL injection, file upload or read, or taking over an administrator account, by an anonymous visitor
10
12 months of Pro
High
Stored XSS by an anonymous visitor, access to other people's bookings or personal data, booking without paying the full price, or a critical issue that needs a subscriber account
5
6 months of Pro
Medium
Issues with real impact that need a subscriber, contributor or author account, reflected XSS, or CSRF that changes data
2
3 months of Pro
Low
Limited impact, issues that need an editor account, or minor information leaks
1
Scoreboard listing with a link to your site
Duplicate
A valid issue that someone else, or we ourselves, reported first
0
Honorable mention with a link to your site
The big one: most points on November 30 wins a lifetime Events Manager Pro license. Ties go to whoever got there first.
The rules
Hunt in the latest released versions of Events Manager, Events Manager Pro and our official add-ons. Our websites, servers and checkout are off limits.
Only test on sites you own, ideally a local or staging copy. Never anyone else's.
Every report needs a working proof of concept with steps we can follow. AI output on its own doesn't count, however convincing it reads.
First valid report wins, going by the time it reached us. Issues we've already logged ourselves count as earlier reports, and we'll show you our record if that happens.
Up to 3 reports waiting for review at a time.
We set the final severity using CVSS and how the issue plays out on a typical site. If we rate it differently from you, we'll explain why.
Keep it private until we've released a fix and 30 days have passed. Going public, or reporting it to another program, before then forfeits the reward.
Pro time goes on the license for your email, or a new license if you don't have one, up to 24 months per person. The lifetime prize is on top.
We won't take legal action over good-faith research that follows these rules.
Reports after November 30 are still welcome, they just don't count towards the lifetime prize.
Doesn't count
Anything that needs administrator access or unfiltered_html on a single site, since administrators can already run code there. Multisite site admins without unfiltered_html are fair game.
Self-XSS, or anything that needs the victim to paste or type the payload themselves.
Missing security headers or cookie flags, and clickjacking on pages without a sensitive action.
Brute force, rate limiting, and username or email enumeration with no further impact.
CSRF on actions with no security impact, such as logging out.
Bugs in WordPress core, other plugins, themes or hosting setups.
Issues that only exist in versions we've already fixed.
Used by Google Analytics to determine which links on a page are being clicked
30 seconds
_ga_
ID used to identify users
2 years
_gid
ID used to identify users for 24 hours after last activity
24 hours
_gat
Used to monitor number of Google Analytics server requests when using Google Tag Manager
1 minute
_gac_
Contains information related to marketing campaigns of the user. These are shared with Google AdWords / Google Ads when the Google Ads and Google Analytics accounts are linked together.
90 days
__utma
ID used to identify users and sessions
2 years after last activity
__utmt
Used to monitor number of Google Analytics server requests
10 minutes
__utmb
Used to distinguish new sessions and visits. This cookie is set when the GA.js javascript library is loaded and there is no existing __utmb cookie. The cookie is updated every time data is sent to the Google Analytics server.
30 minutes after last activity
__utmc
Used only with old Urchin versions of Google Analytics and not with GA.js. Was used to distinguish between new sessions and visits at the end of a session.
End of session (browser)
__utmz
Contains information about the traffic source or campaign that directed user to the website. The cookie is set when the GA.js javascript is loaded and updated when data is sent to the Google Anaytics server
6 months after last activity
__utmv
Contains custom information set by the web developer via the _setCustomVar method in Google Analytics. This cookie is updated every time new data is sent to the Google Analytics server.
2 years after last activity
__utmx
Used to determine whether a user is included in an A / B or Multivariate test.